Belgian hospital cyberattack disrupts services and forces transfers as systems are shut down
A cyberattack on AZ Monica hospital in Antwerp disrupted computer systems, leading to canceled surgeries and reduced emergency capacity. The incident highlights how ransomware-style disruptions can quickly cascade into real-world healthcare delays and patient transfers.
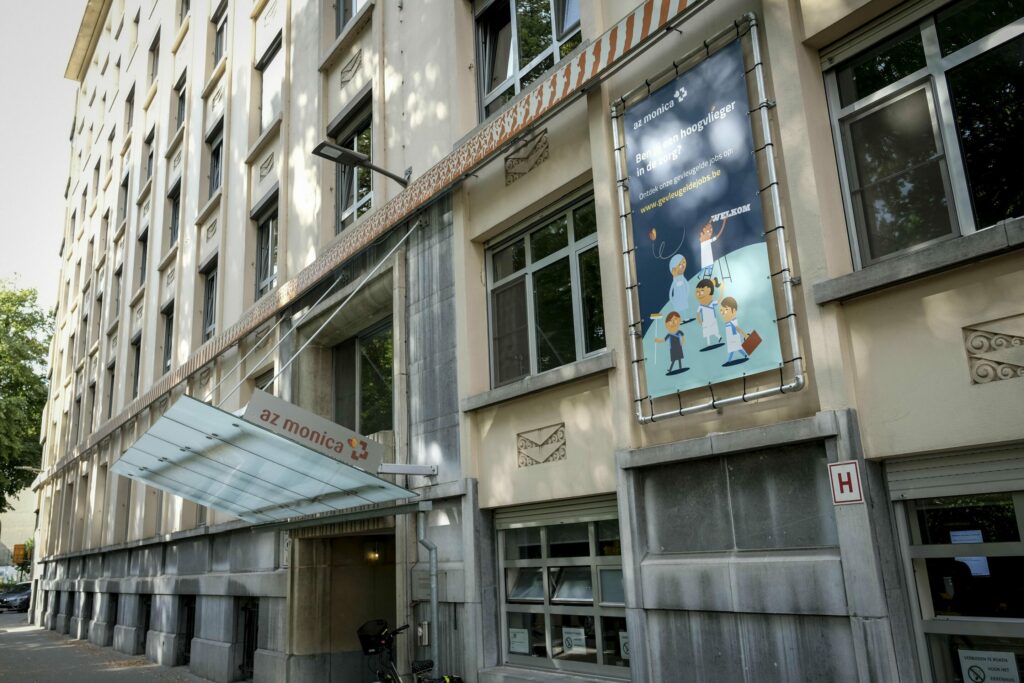
A hospital network hit, services scaled back
A cyberattack that began on January 13, 2026, disrupted computer systems at AZ Monica hospital in Antwerp, forcing administrators to shut down servers at its Antwerp and Deurne campuses while teams investigated the incident. The immediate effect was operational: digital workflows were interrupted, staff had to switch to contingency procedures, and hospital capacity was constrained at a moment when rapid coordination is often critical.
According to reporting summarized in public references, the disruption led to the cancellation of surgeries and created delays and bottlenecks in patient registration and routine administrative processes. Several patients were transferred to other facilities, including critical cases, and emergency operations were reportedly reduced, with guidance to the public to use alternative medical options where appropriate.
Why healthcare cyberattacks are uniquely dangerous
When hospitals lose access to IT systems—even temporarily—the impact extends far beyond email outages. Clinical scheduling, lab results, radiology images, medication administration records, ambulance coordination and staff paging systems can all be intertwined with network availability. That means a cybersecurity event can translate into postponed care, longer waits and harder triage decisions.
Hospitals often face a difficult trade-off during an attack: keep systems online to preserve continuity of care, or take systems offline to prevent further compromise and protect patient data. In many incidents, administrators choose partial shutdowns to limit spread, then rebuild services step-by-step to regain control.
Investigations and recovery
The specific cause and the identity of the attackers were not immediately clear in early public summaries. Typically, responders aim first to stabilize operations, then to determine whether data exfiltration occurred, whether malware persists, and whether backups and restoration pathways are intact. Law enforcement and national cybersecurity agencies may be involved depending on the scale and suspected origin.
The Antwerp incident adds to a broader pattern: healthcare remains a high-value target because downtime is costly and time-sensitive services increase pressure to resolve disruptions quickly. The case is likely to renew calls for stronger segmentation of hospital networks, faster patching cycles for medical devices and servers, and regular tabletop exercises that test how staff can run critical services safely during an IT blackout.